Play the games

12 true stories

The greatest hacks in history.

12 hacks that shook the world, how each one worked, and the one lesson in it for you.

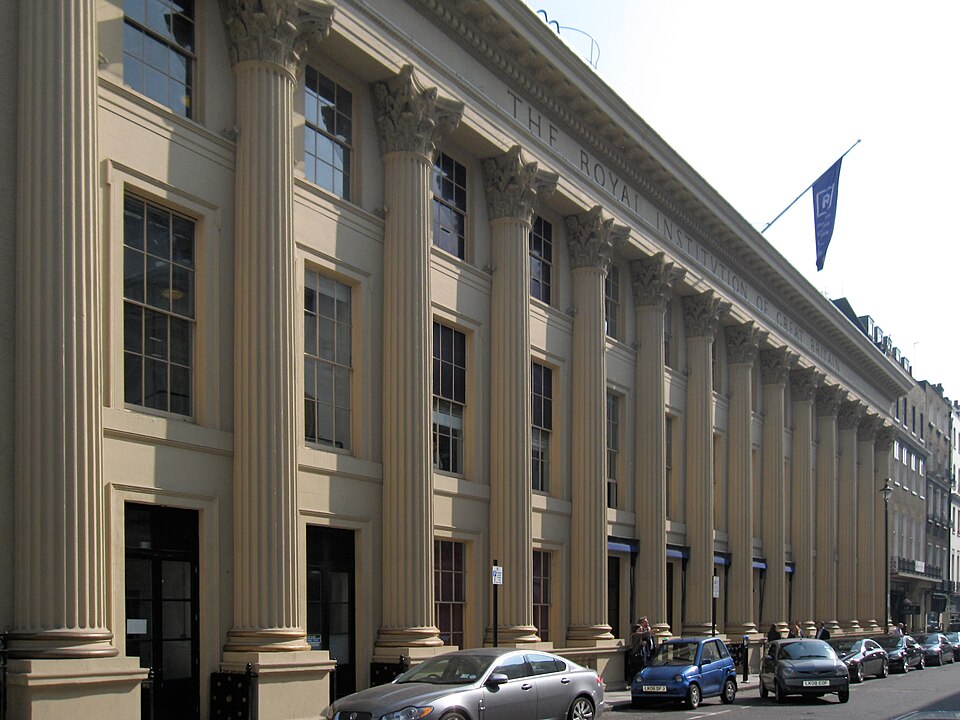
  1. The columned front of the Royal Institution on Albemarle Street, London.
    The Royal Institution in London, where the 1903 wireless demo was hijacked. Photo: Gryffindor, CC BY-SA 3.0

    1903

    United Kingdom

    The magician who hacked the wireless

    Marconi said nobody could listen in on his wireless messages. A magician proved him wrong in front of a crowd.

    How it worked

    1. 1Marconi’s team ran a public demo at London’s Royal Institution, receiving Morse code by radio.
    2. 2Instead of the expected message, the receiver tapped out ‘rats’ over and over, then a rude rhyme.
    3. 3Magician Nevil Maskelyne had beamed it in, to prove anyone could butt in on the airwaves.
    The haulOne rude ditty, beamed into Marconi’s big public demo

    What happened next: Marconi’s man Fleming called it ‘scientific hooliganism’. Maskelyne owned up, citing the public good.

    The lesson ‘Totally private’ is a sales pitch, not a promise. Be careful what you share.
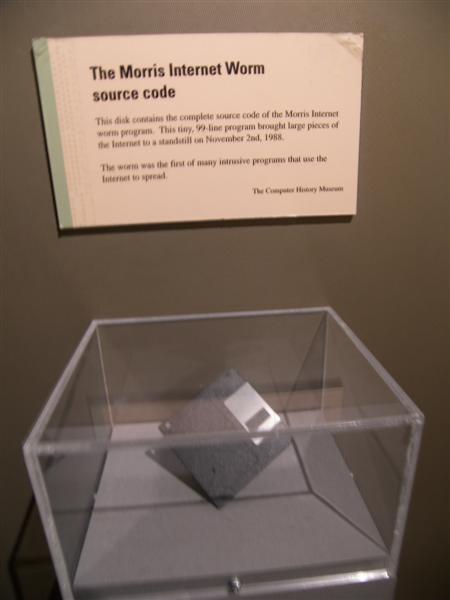
  2. A floppy disk holding the Morris worm’s source code, in a museum display.
    The floppy disk holding the Morris worm’s code, on show at Boston’s Museum of Science. Photo: Go Card USA from Boston, USA, CC BY-SA 2.0

    1988

    November · United States

    The worm that jammed the internet

    A student’s sneaky program copied itself across the young internet far faster than he’d imagined.

    How it worked

    1. 1It slipped into computers through well known holes in their software, like a mail program.
    2. 2Then it went password hunting, trying people’s usernames and a list of 432 common passwords.
    3. 3A coding slip let copies pile up on each machine until the computers ground to a halt.
    The haulBetween 5 and 10% of computers on the internet put out of action

    What happened next: It was traced to Cornell student Robert Tappan Morris, who was sentenced to three years’ probation.

    The lesson Never use your name, username or a common word as a password. Those get tried first.

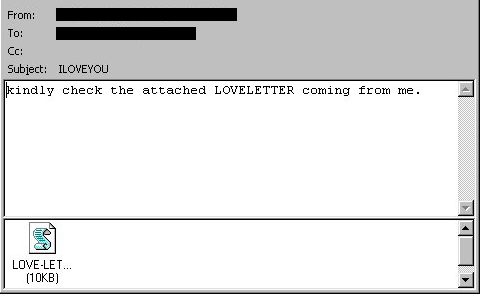
  3. A screenshot of an ILOVEYOU email with its love letter attachment.
    An ILOVEYOU email, with the ‘love letter’ attachment that unleashed the virus. Public domain (Mario23)

    2000

    4 May · Worldwide

    The email that said ILOVEYOU

    Millions got a love letter by email from someone they knew. Opening it unleashed a virus.

    How it worked

    1. 1An email arrived from a friend or workmate with a ‘love letter’ attached.
    2. 2Opening it let a virus wreck files and steal passwords on the computer.
    3. 3Then it emailed itself to everyone in the address book, and spread around the globe in a day.
    The haulReportedly 45 million computers infected within 24 hours

    What happened next: The Philippines had no hacking law, so no one was ever prosecuted. Its maker later owned up.

    The lesson Don’t open surprise attachments, even from friends. Check with them another way first.

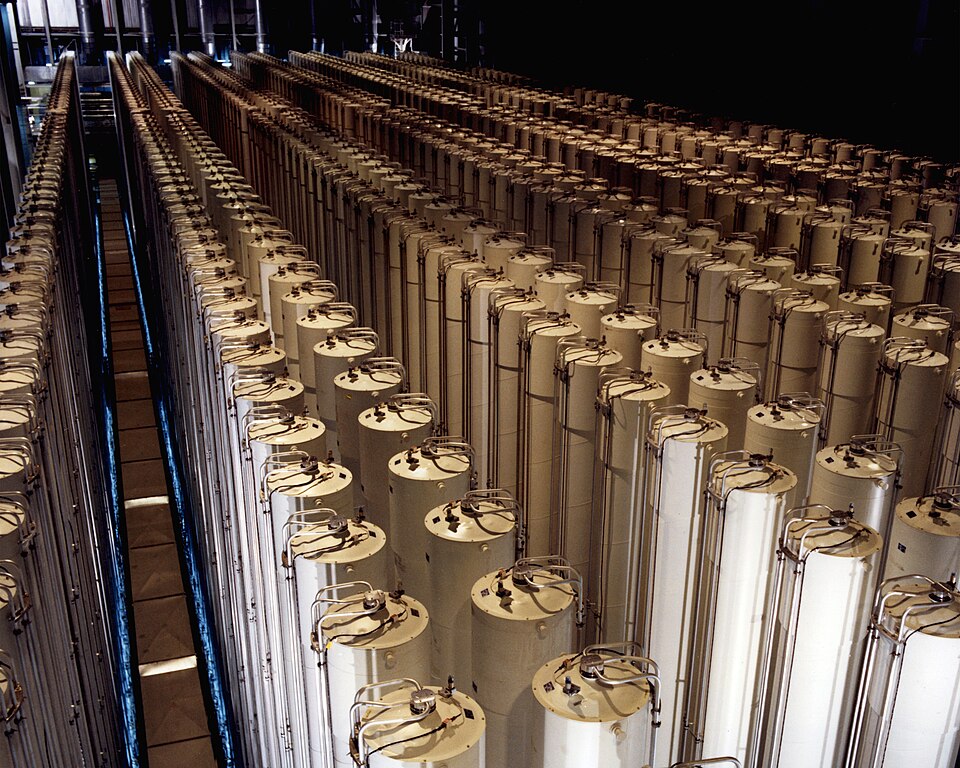
  4. Rows of tall gas centrifuges in a uranium enrichment plant.
    Uranium centrifuges at a US plant, the kind of machine Stuxnet wrecked in Iran. Public domain (US Department of Energy)

    2010

    Iran

    Stuxnet, the virus that broke machines

    A computer virus got inside a nuclear plant cut off from the internet, and quietly wrecked its machines.

    How it worked

    1. 1The Natanz plant wasn’t on the internet, so the virus most likely came in on a USB stick.
    2. 2It made the plant’s centrifuges, machines that spin very fast, speed up and slow down.
    3. 3All the while, it fed the control room readings that said everything was normal.
    The haulAbout 1,000 of Iran’s 5,000 centrifuges destroyed, by estimates

    What happened next: Reports say the US and Israel built it. It set Iran’s program back by an estimated two years.

    The lesson Never plug in a USB stick you found, or one handed to you by someone you don’t know.

  5. Yahoo’s headquarters campus near Mathilda Avenue in Sunnyvale, California.
    Yahoo’s headquarters in Sunnyvale, California. Photo: Coolcaesar, CC BY-SA 3.0

    2013

    August · Worldwide

    All 3 billion Yahoo accounts

    Hackers raided Yahoo in 2013. Four years on, it turned out they’d hit every single account.

    How it worked

    1. 1In August 2013, thieves got into Yahoo’s systems and made off with its user records.
    2. 2They took names, email addresses and passwords, though not bank or card details.
    3. 3Yahoo’s first count, in 2016, was a third of the truth. It was every account it had.
    The haulThree billion accounts, every single one Yahoo had

    What happened next: Verizon, which had just bought Yahoo’s main business for US$4.48 billion, revealed the full scale in 2017.

    The lesson Use a different password for every account, so one leak can’t unlock the rest.

  6. The tall Bangladesh Bank building in the Motijheel business district of Dhaka.
    Bangladesh Bank in Dhaka. Hackers tried to empty its account in New York. Photo: ASaber91, CC BY 2.0

    2016

    February · Bangladesh

    The Bangladesh Bank heist

    Hackers tried to empty Bangladesh’s central bank account in New York. A spelling slip saved part of it.

    How it worked

    1. 1A year earlier, hackers slipped into the bank’s computers with a fake job application email.
    2. 2One Thursday night, just before the weekend, they ordered US$951 million moved out of New York.
    3. 3A spelling mistake stopped a US$20 million transfer, but US$81 million still got away.
    The haulUS$81 million stolen

    What happened next: The FBI traced it to North Korea’s Lazarus hackers. About US$65 million is thought to be still missing.

    The lesson Spelling slips are a classic giveaway. Read names and details slowly before sending money.

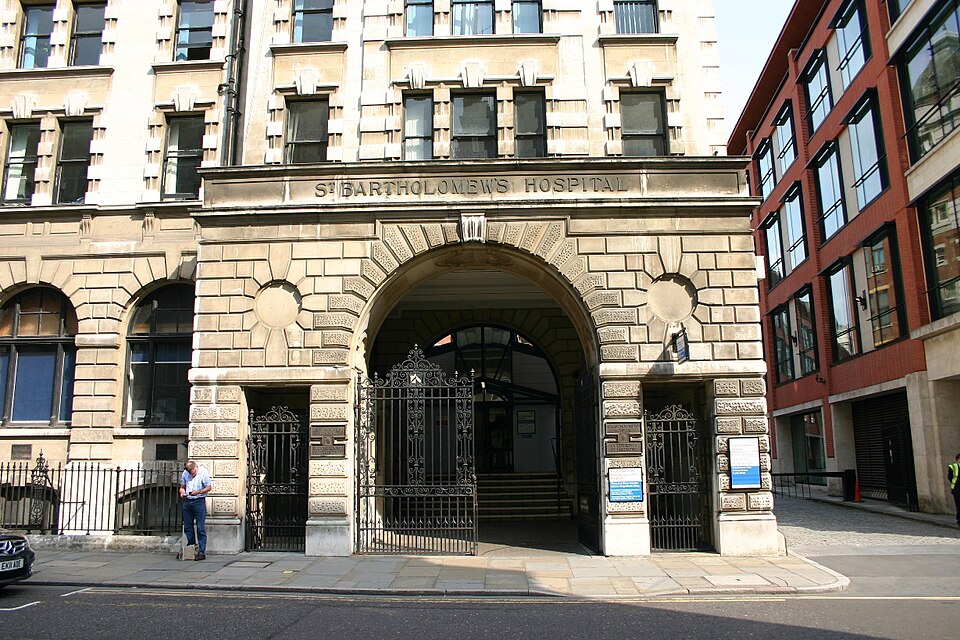
  7. The stone entrance of St Bartholomew’s Hospital in London.
    St Bartholomew’s Hospital in London. Its NHS trust was one of many hit by WannaCry in May 2017. Photo: Luca Borghi, CC BY-SA 4.0

    2017

    12 May · United Kingdom

    WannaCry locks up the NHS

    A virus froze computers across England’s NHS. Warnings to fix the weak spot went out weeks earlier.

    How it worked

    1. 1WannaCry is ransomware: it scrambles the files on a computer so nobody can open them.
    2. 2It hit computers running old Windows, or Windows missing its latest fixes.
    3. 3Alerts telling NHS bodies to install the fix went out in March and April. Many weren’t acted on.
    The haulOver 19,000 appointments cancelled, by NHS England’s estimate

    What happened next: A researcher hit a ‘kill switch’ that stopped it. Auditors said basic IT security could have prevented it.

    The lesson Install updates when your device asks. They fix the very holes attackers use.

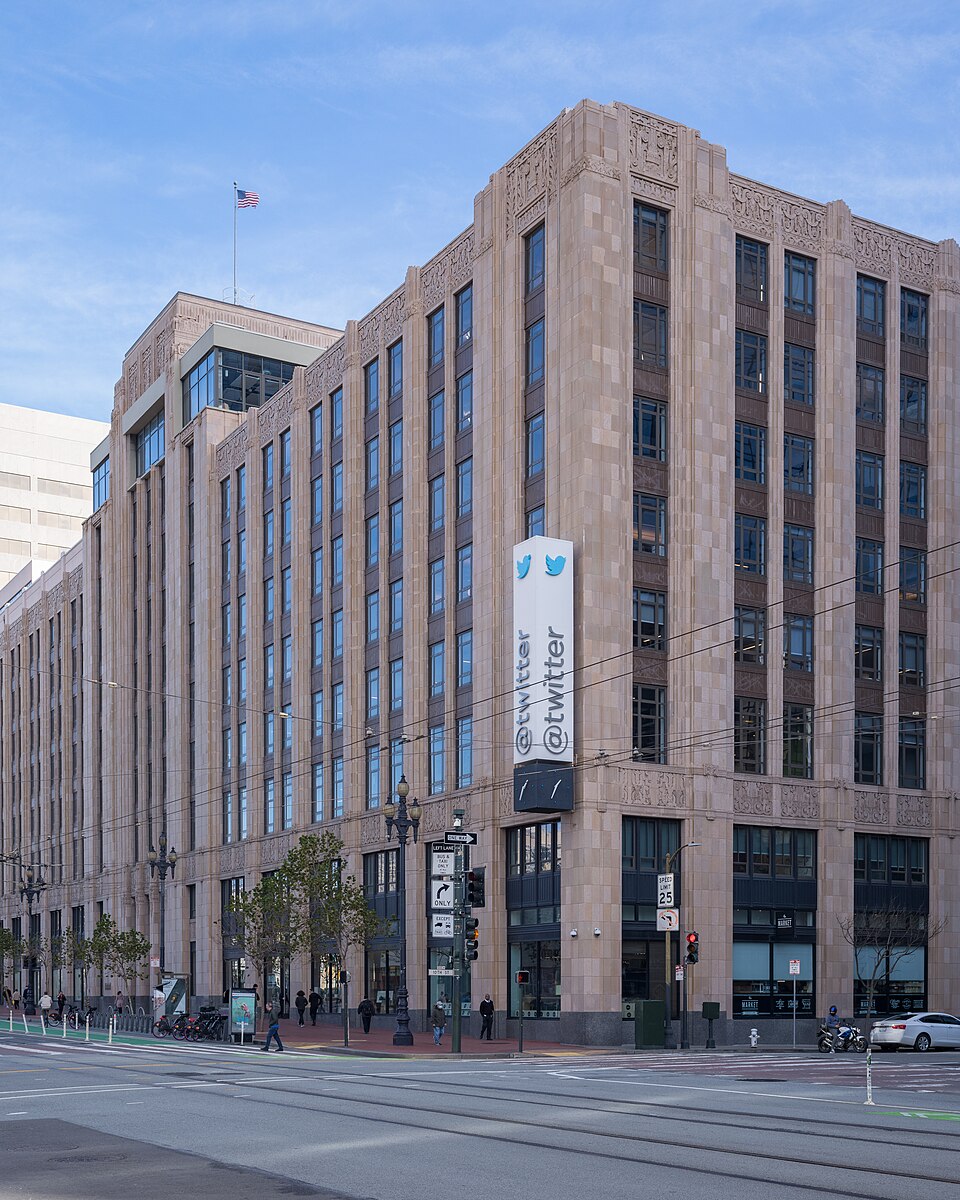
  8. The Twitter headquarters building on Market Street in San Francisco.
    Twitter’s headquarters in San Francisco, photographed in early 2023. Photo: Frank Schulenburg, CC BY-SA 4.0

    2020

    15 July · United States

    The Twitter celebrity bitcoin hack

    Obama, Elon Musk and Apple all tweeted the same ‘double your bitcoin’ offer. A teenager was behind it.

    How it worked

    1. 1Hackers rang Twitter staff working from home, pretending to be the company’s IT help desk.
    2. 2They sent staff to a fake login page that looked just like the real one, and grabbed their details.
    3. 3Using Twitter’s own tools, they seized 130 accounts and tweeted a bitcoin scam from 45.
    The haulAbout US$118,000 in bitcoin taken, and 130 accounts hijacked

    What happened next: Three people were arrested within weeks, including the teenage ringleader.

    The lesson ‘Send crypto and get double back’ is always a scam, even from a famous account.

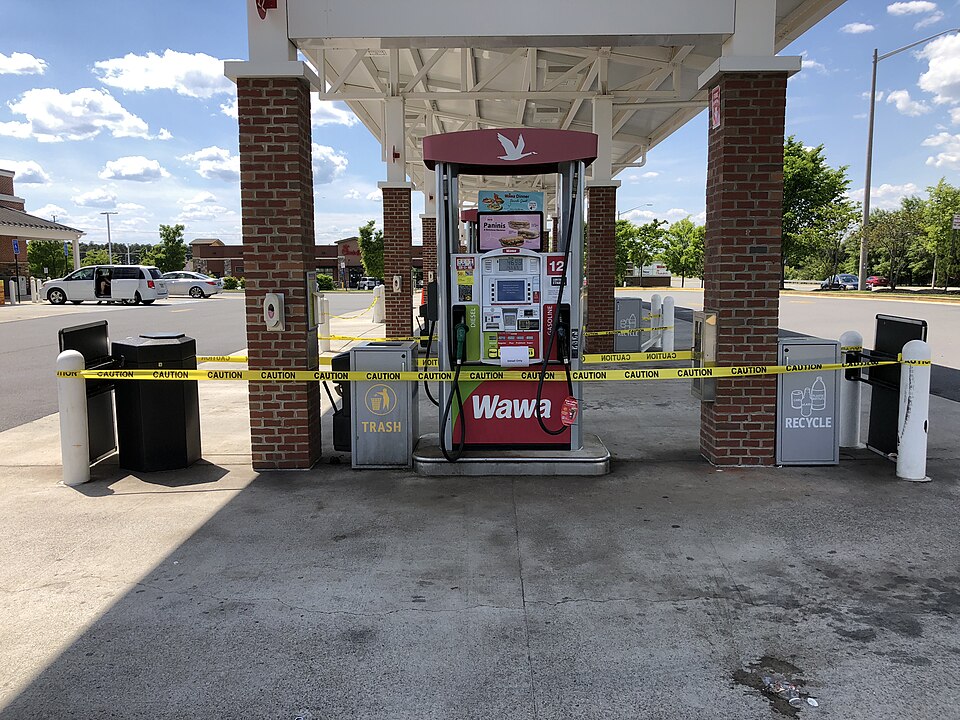
  9. Fuel pumps marked out of service at a service station in Virginia during the May 2021 shortage.
    Fuel pumps out of action in Virginia during the May 2021 panic buying. Photo: Famartin, CC BY-SA 4.0

    2021

    May · United States

    The password that shut a pipeline

    One stolen password led to a major US fuel pipeline shutting down, and drivers rushed to fill up.

    How it worked

    1. 1Hackers got the password to an old remote login, used to reach the network from outside.
    2. 2That login needed only the password, with no second check like a code sent to a phone.
    3. 3Inside, the DarkSide gang struck with ransomware, and the company shut the pipeline for days.
    The haulA 75 bitcoin ransom, plus panic buying at petrol stations

    What happened next: Colonial paid the ransom. US officials later clawed back about US$2.3 million of it.

    The lesson Turn on two step login, so a stolen password alone can’t get anyone in.

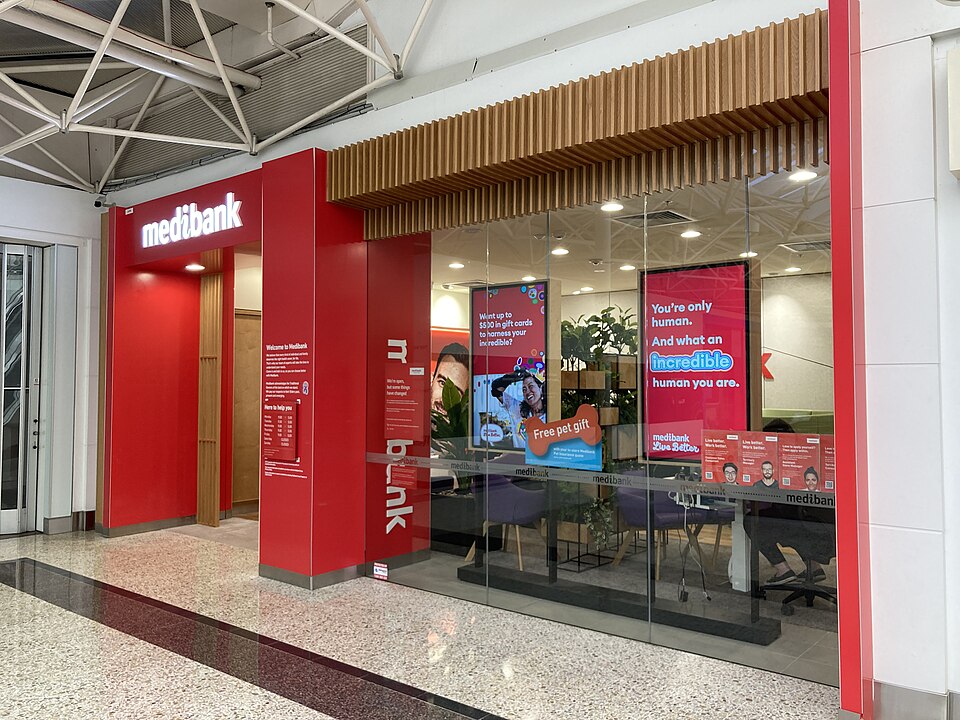
  10. A Medibank shopfront inside the Westfield Woden shopping centre in Canberra.
    A Medibank branch in Canberra in July 2022, months before the hack. Photo: Nick-D, CC BY-SA 4.0

    2022

    Australia

    The saved password that leaked Medibank

    One worker saved his logins in his web browser. Hackers used them to raid an Aussie health insurer.

    How it worked

    1. 1A contractor saved his Medibank logins in his browser, which synced them to his home computer.
    2. 2Malware on that home computer stole the saved passwords and passed them to hackers.
    3. 3Medibank’s remote login asked for no second check, so the hackers walked straight in.
    The haul520GB of data on 9.7 million customers, dumped on the dark web

    What happened next: Australia, the UK and the US sanctioned a Russian man, Aleksandr Ermakov, over the attack.

    The lesson Passwords saved in your browser are only as safe as every computer they sync to.

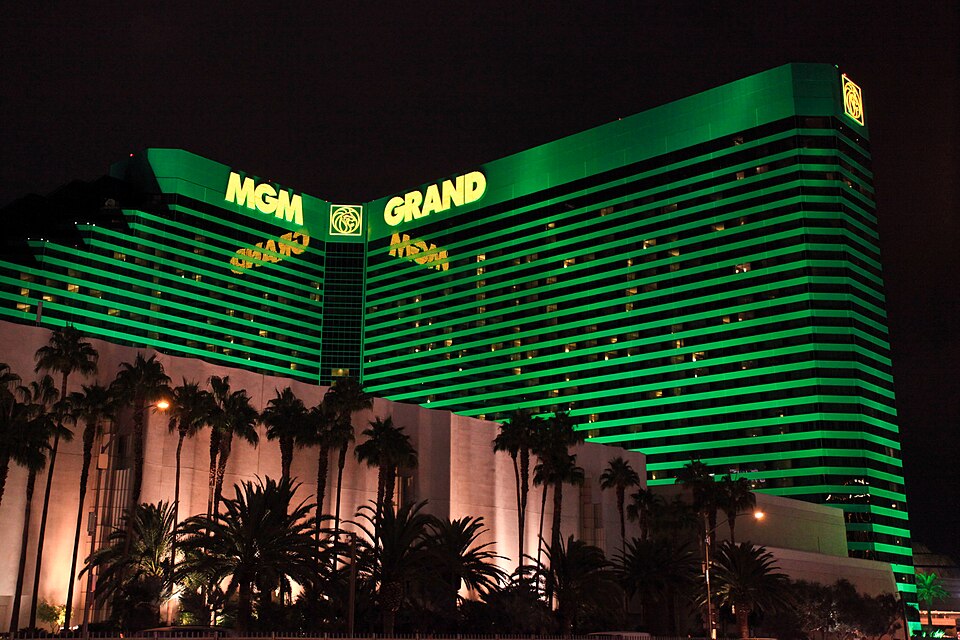
  11. The green glass MGM Grand hotel and casino in Las Vegas, lit up at night.
    MGM Grand on the Las Vegas Strip, one of the casinos hit in 2023. Photo: Håkan Dahlström, CC BY 2.0

    2023

    September · United States

    The phone call that froze MGM’s casinos

    Hackers say one phone call, just 10 minutes long, was all it took to cripple a Las Vegas casino giant.

    How it worked

    1. 1The hackers say they found an MGM employee on LinkedIn, the work networking site.
    2. 2Then they rang the IT help desk pretending to be that person, and talked their way in.
    3. 3No clever code was needed for the way in. A convincing voice and a few facts did the job.
    The haulSlot machines shut down across MGM’s Las Vegas Strip casinos

    What happened next: MGM reportedly refused to pay the hackers, and its systems stayed down for days.

    The lesson Anyone can pretend to be anyone on the phone. Never give a caller your passwords or codes.

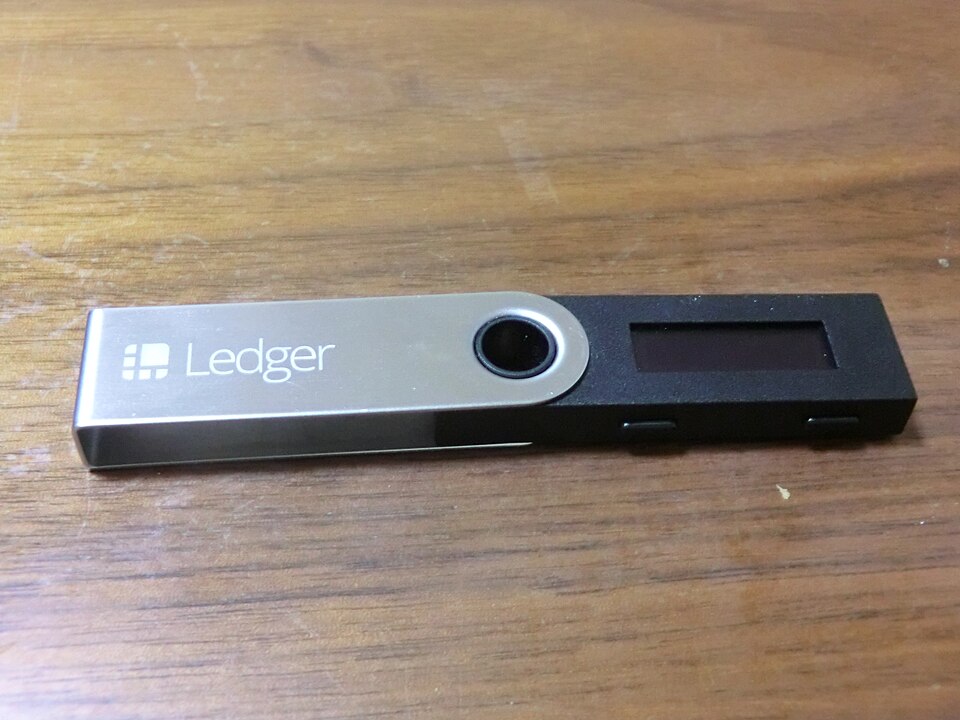
  12. A Ledger hardware crypto wallet on a wooden table.
    A hardware crypto wallet. Bybit kept its coins offline like this, and hackers still tricked staff into signing them away. Photo: Motokoka, CC BY-SA 4.0

    2025

    21 February · United Arab Emirates

    The US$1.5 billion crypto heist

    Bybit staff approved what looked like a routine transfer. North Korean hackers walked off with US$1.5 billion.

    How it worked

    1. 1Bybit staff signed off a ‘routine’ transfer from their offline ‘cold’ wallet, as usual.
    2. 2But the signing screen had been rigged to hide what they were really approving.
    3. 3That approval quietly changed the wallet’s rules and handed the hackers control of it.
    The haulMore than US$1.5 billion in ether, the biggest exchange hack yet

    What happened next: Experts quickly blamed North Korea’s Lazarus hackers. The wallet maker, Safe, paused some features.

    The lesson Screens can be faked. Before you approve any payment, check the details another way.

The greatest scams in history.

Same idea, the other side of the story.

Read it

Stay unscammable.

Get a weekly email with scam and hack stories you wouldn’t believe.